Cloud environments change fast. Hundreds of resources are created, modified, and decommissioned every week, and every one of those changes can quietly introduce a misconfiguration that exposes data. Cloud Security Posture Management (CSPM) exists to catch those mistakes continuously, before an attacker does.
What CSPM Actually Does
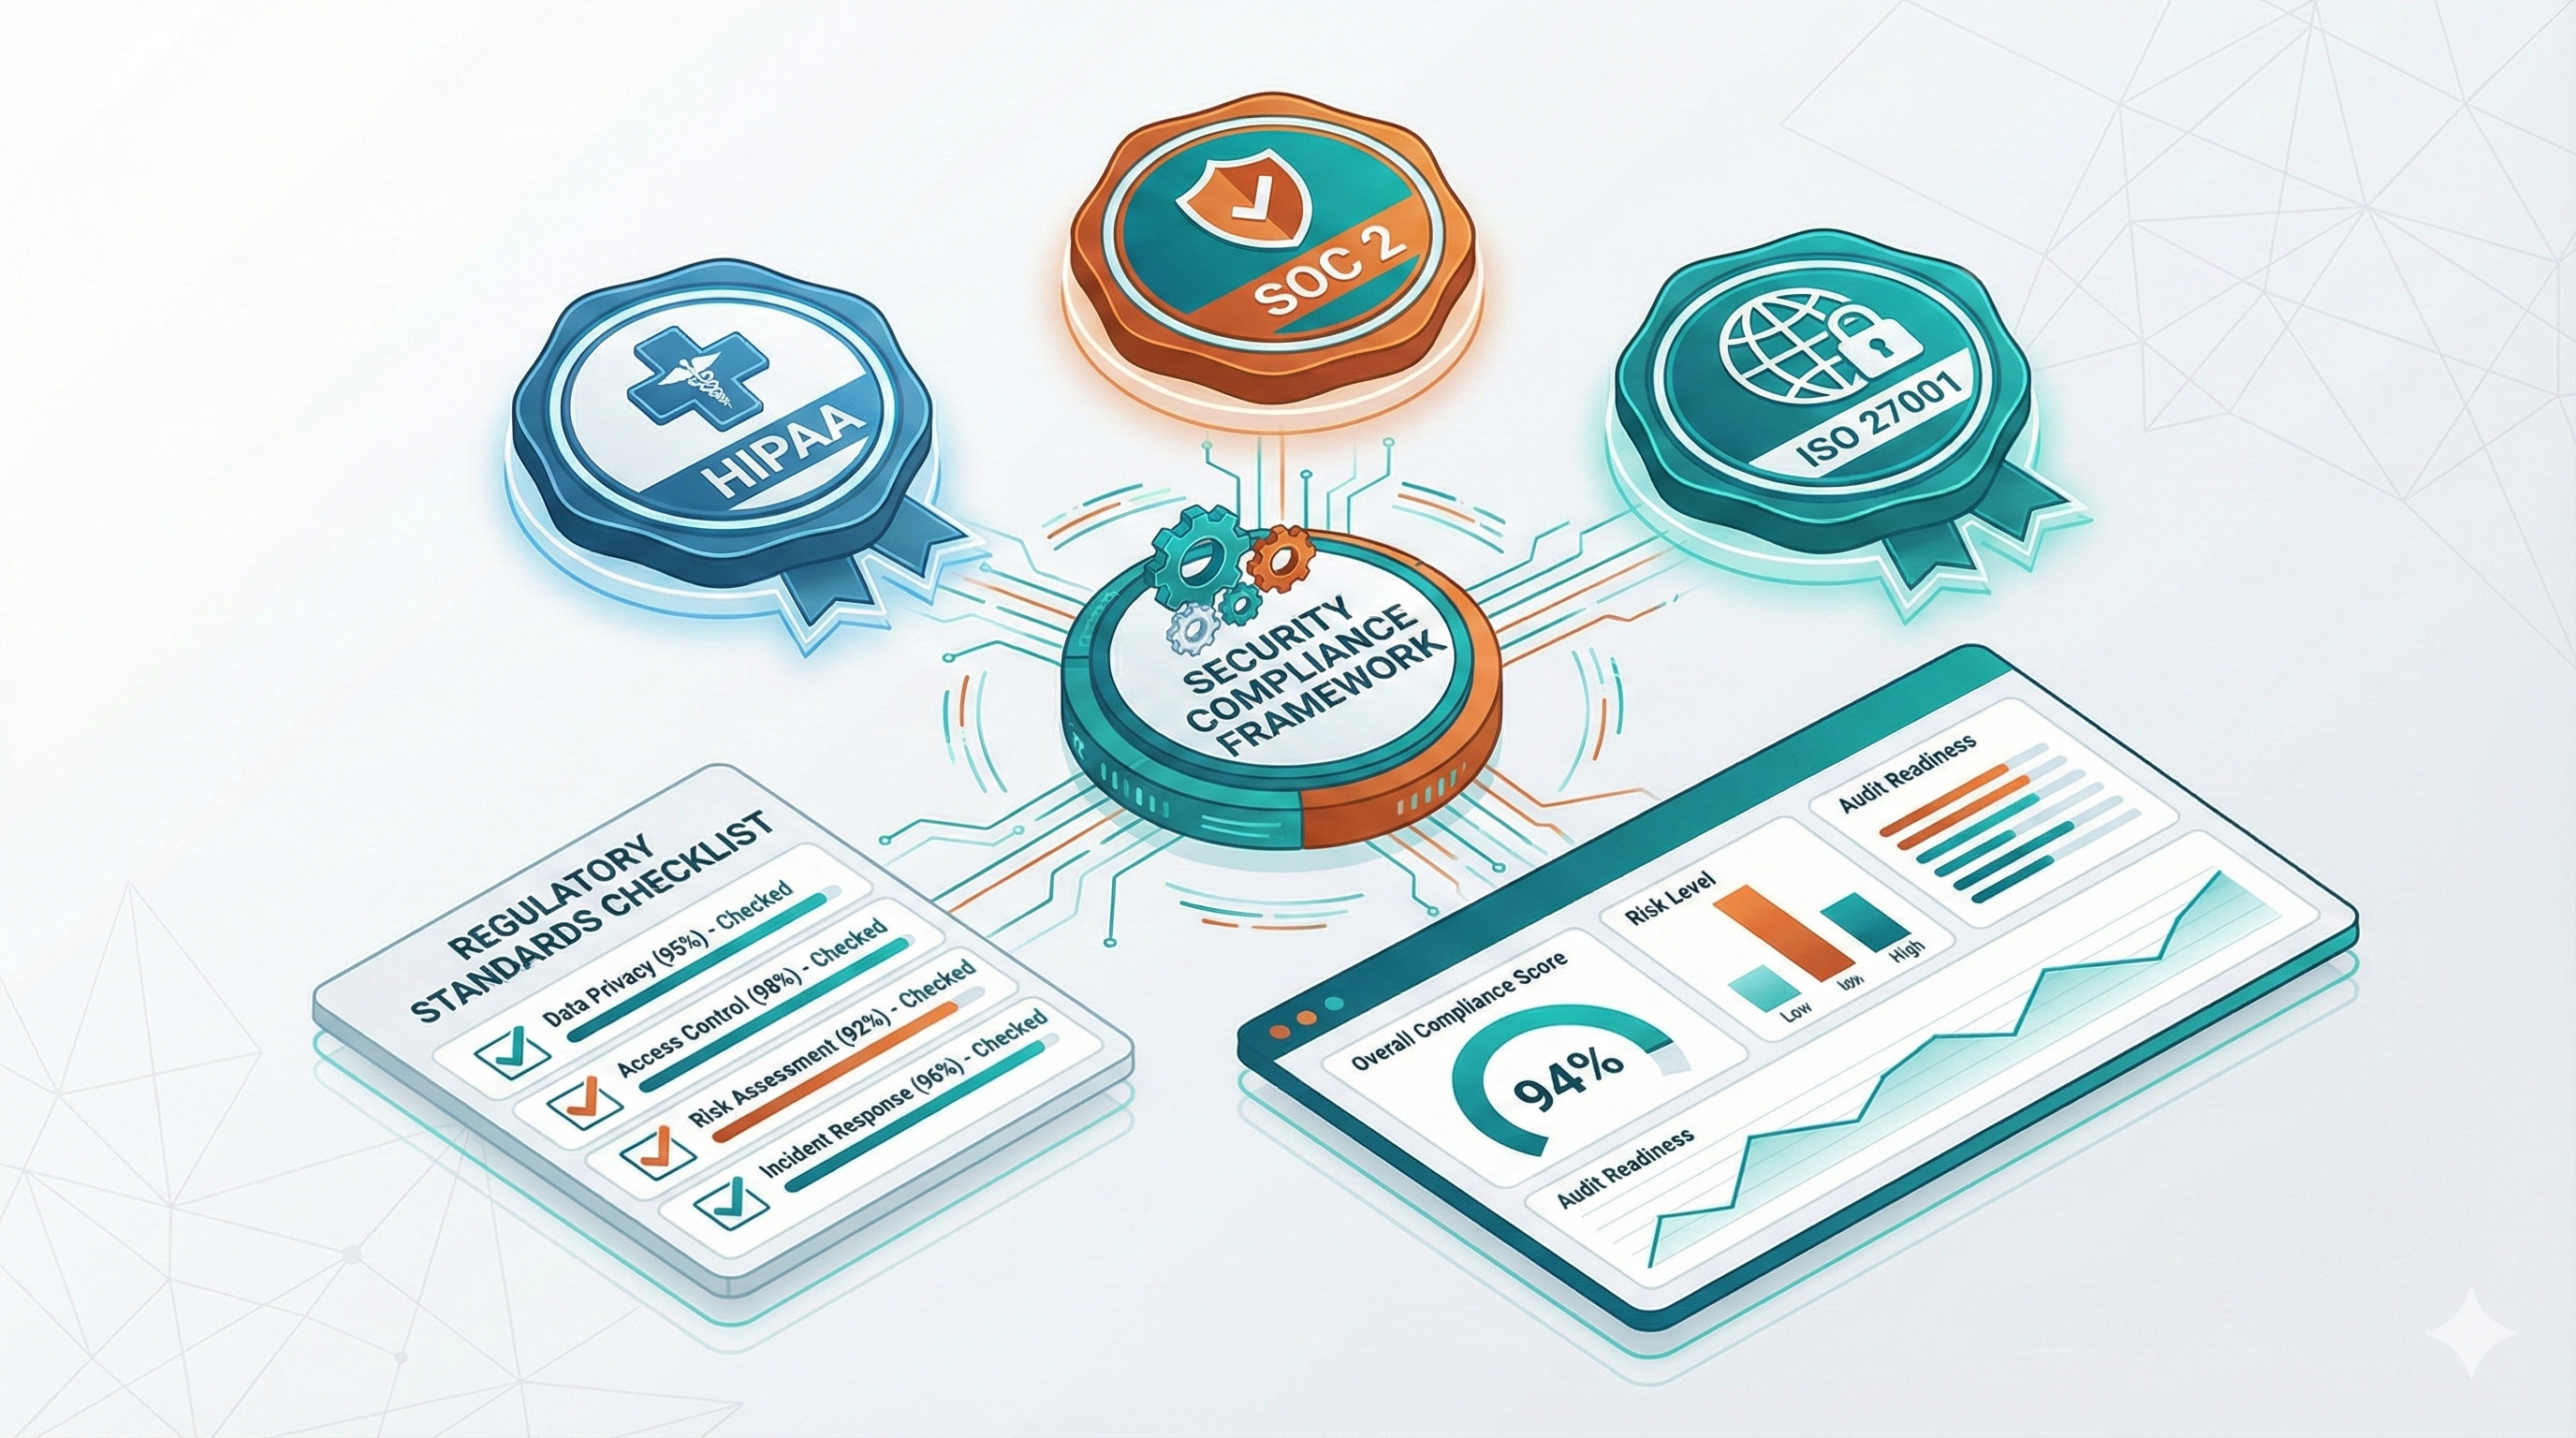
CSPM tools continuously inspect your cloud accounts against security benchmarks such as the CIS Foundations Benchmarks, NIST 800-53, and the provider's own best-practice frameworks. They detect public storage buckets, over-permissive IAM roles, unencrypted databases, disabled logging, and exposed management ports, then rank findings by real-world risk.
Why Misconfigurations Dominate Incidents
Industry research consistently attributes the majority of cloud breaches to customer-side misconfiguration rather than provider failure. The identity layer is the most common culprit: over-privileged service accounts, long-lived access keys, and forgotten cross-account trusts. CSPM gives you a single, normalized view of that identity sprawl across AWS, Azure, and GCP.
Building a Practical CSPM Program
A tool alone is not a program. Start by defining the guardrails that matter for your organization: where data may live, which services are banned, which identities may do what. Encode those rules as policies in your CSPM, route critical findings to the teams that own the affected accounts, and measure time-to-remediation rather than raw finding counts.
Infrastructure as Code as the Real Fix
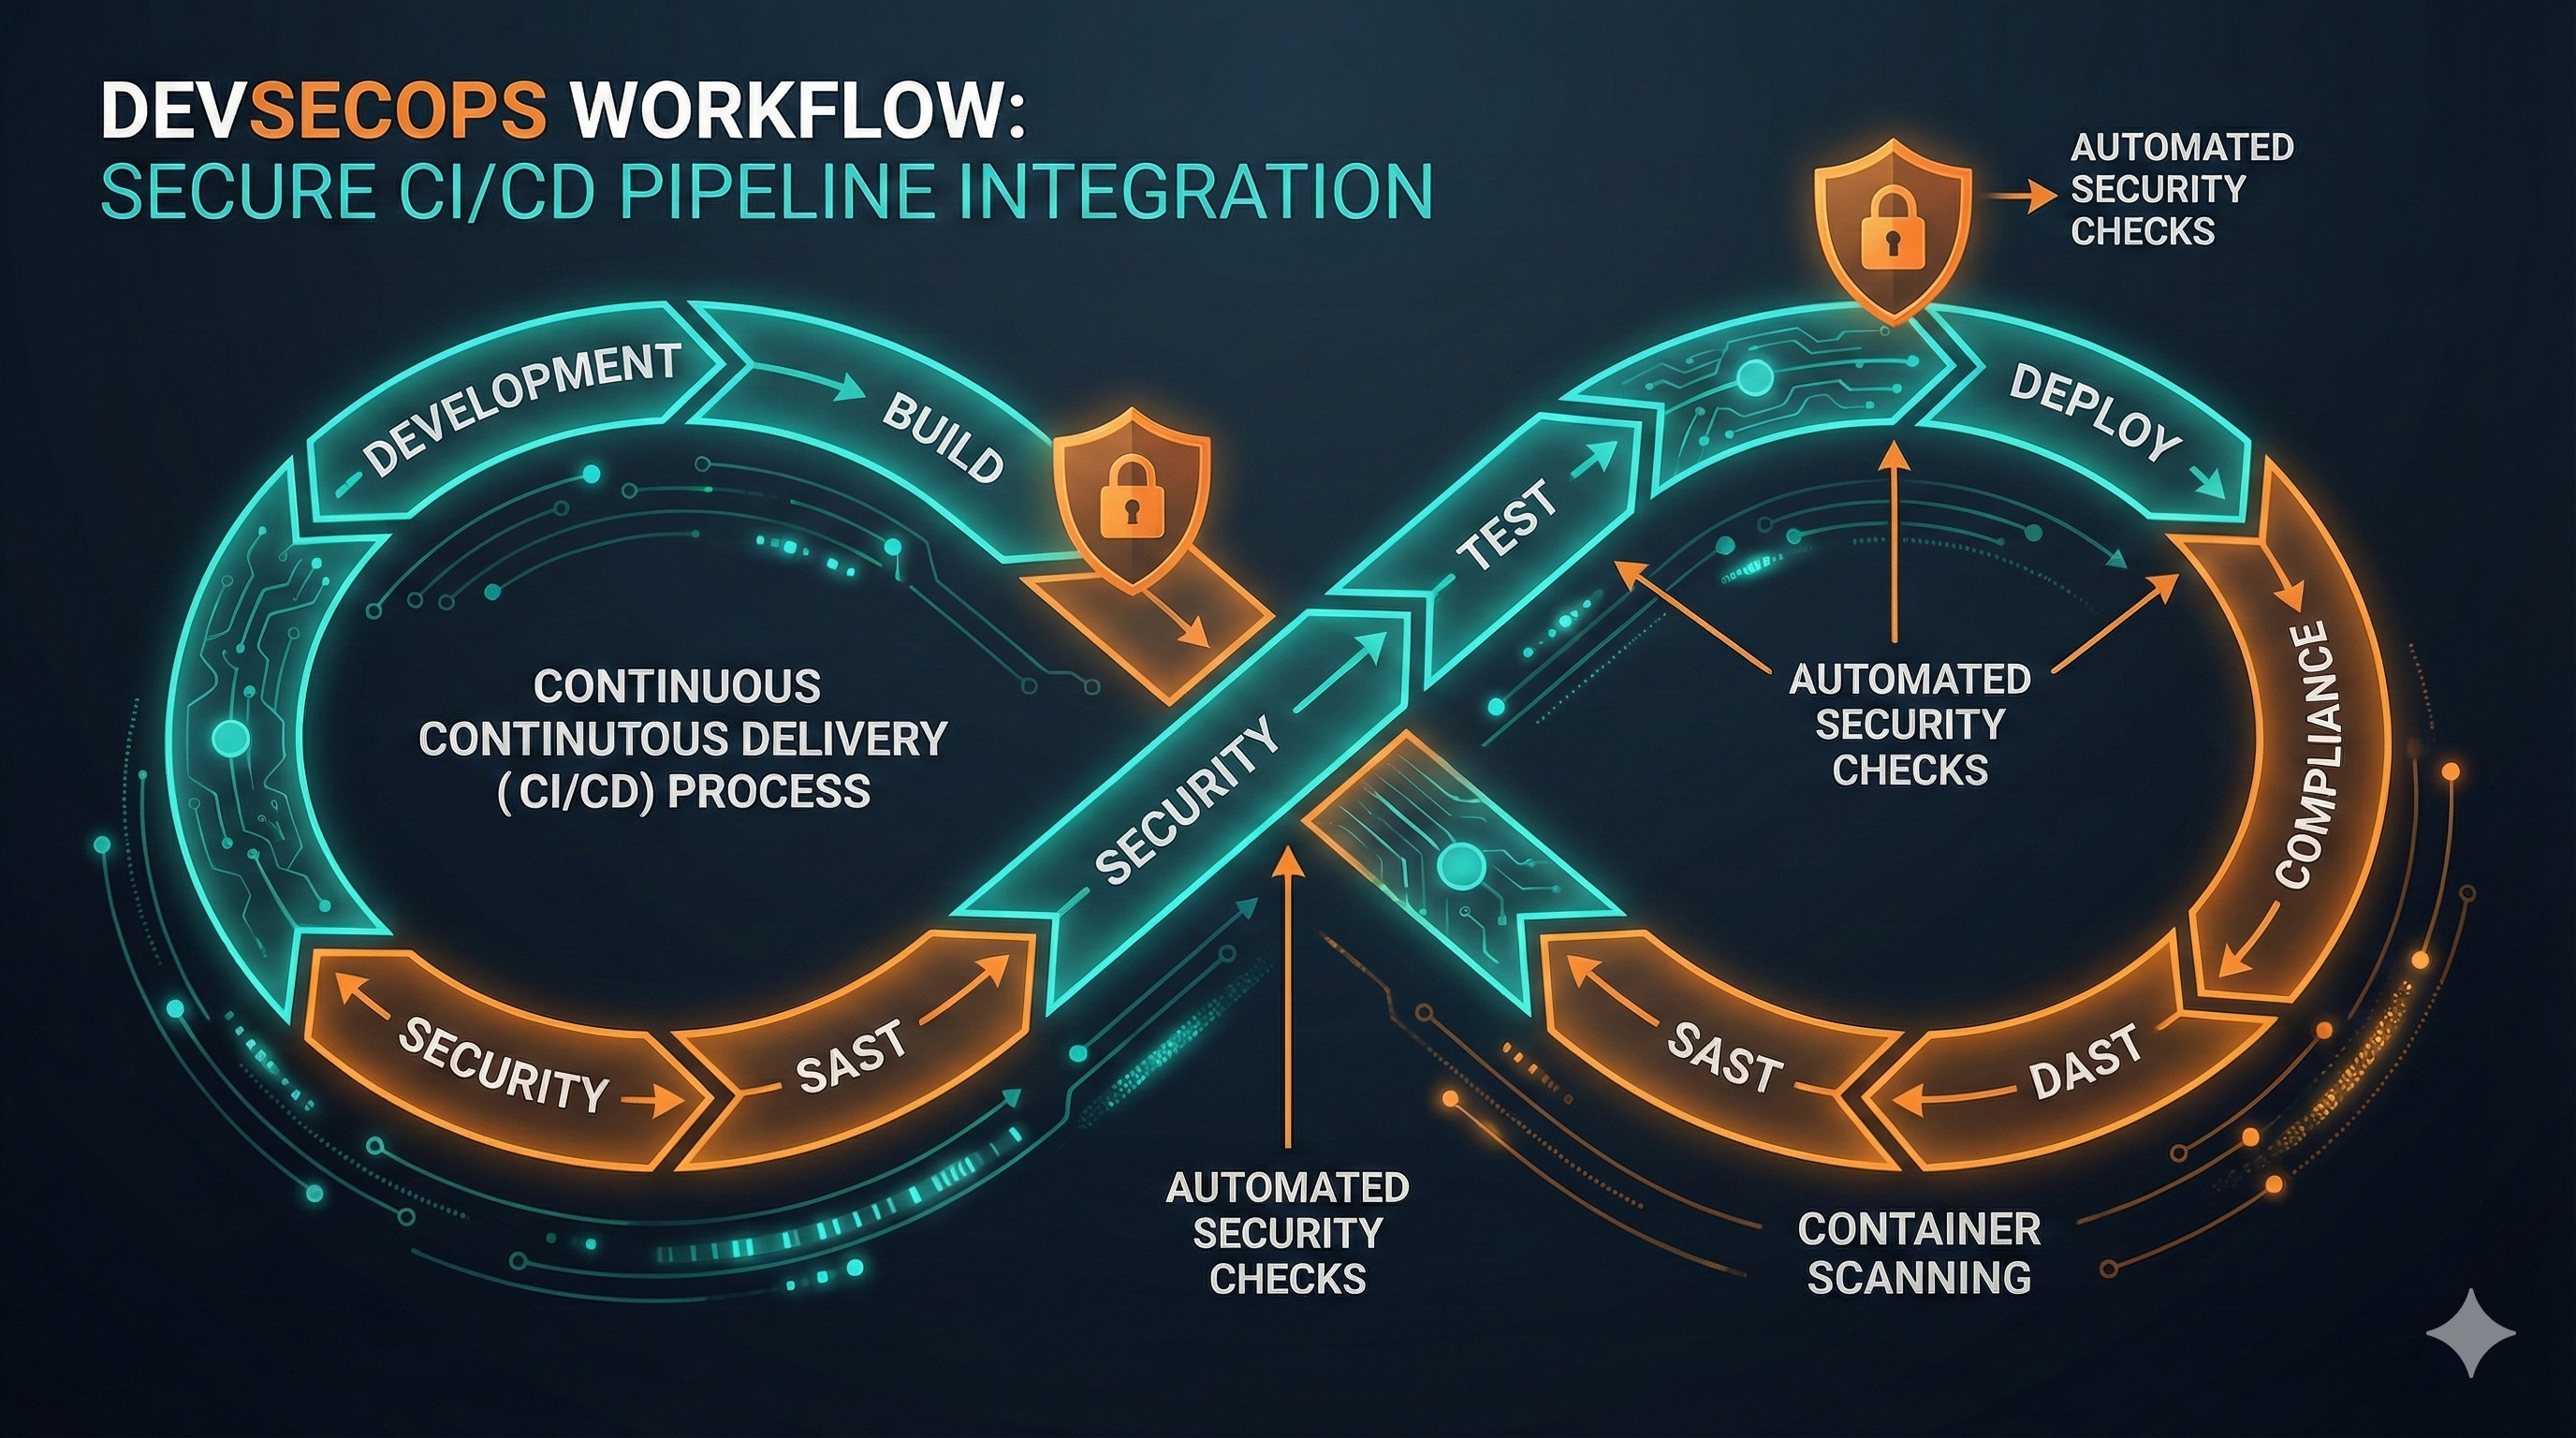
The most mature posture programs push fixes upstream. Scan Terraform, CloudFormation, and Kubernetes manifests at pull-request time so misconfigurations never reach production. Treat your CSPM production findings as lessons that become new pre-deployment policy checks.
Getting Started
Enable the native posture tools first (AWS Security Hub, Azure Secure Score, GCP Security Command Center) to get immediate visibility, then evaluate dedicated CSPM platforms as your multi-cloud footprint grows. If you want an experienced second opinion on your cloud posture, our cloud security team can help.