For organizations in healthcare, finance, and other regulated sectors, security compliance is a permanent operating condition, not a one-time project. Frameworks like HIPAA, PCI DSS, SOC 2, and ISO 27001 overlap heavily, yet most teams treat each audit as a separate scramble.
Map Controls Once, Comply Many Times
The most effective strategy is to build a single internal control library and map it to every framework you answer to. Encryption at rest, access reviews, logging, and incident response appear in all of them with minor wording differences. Implement the strictest version once, then reuse the evidence for every audit. This turns five annual audits into one continuous program with five reporting views.
Automate Evidence Collection
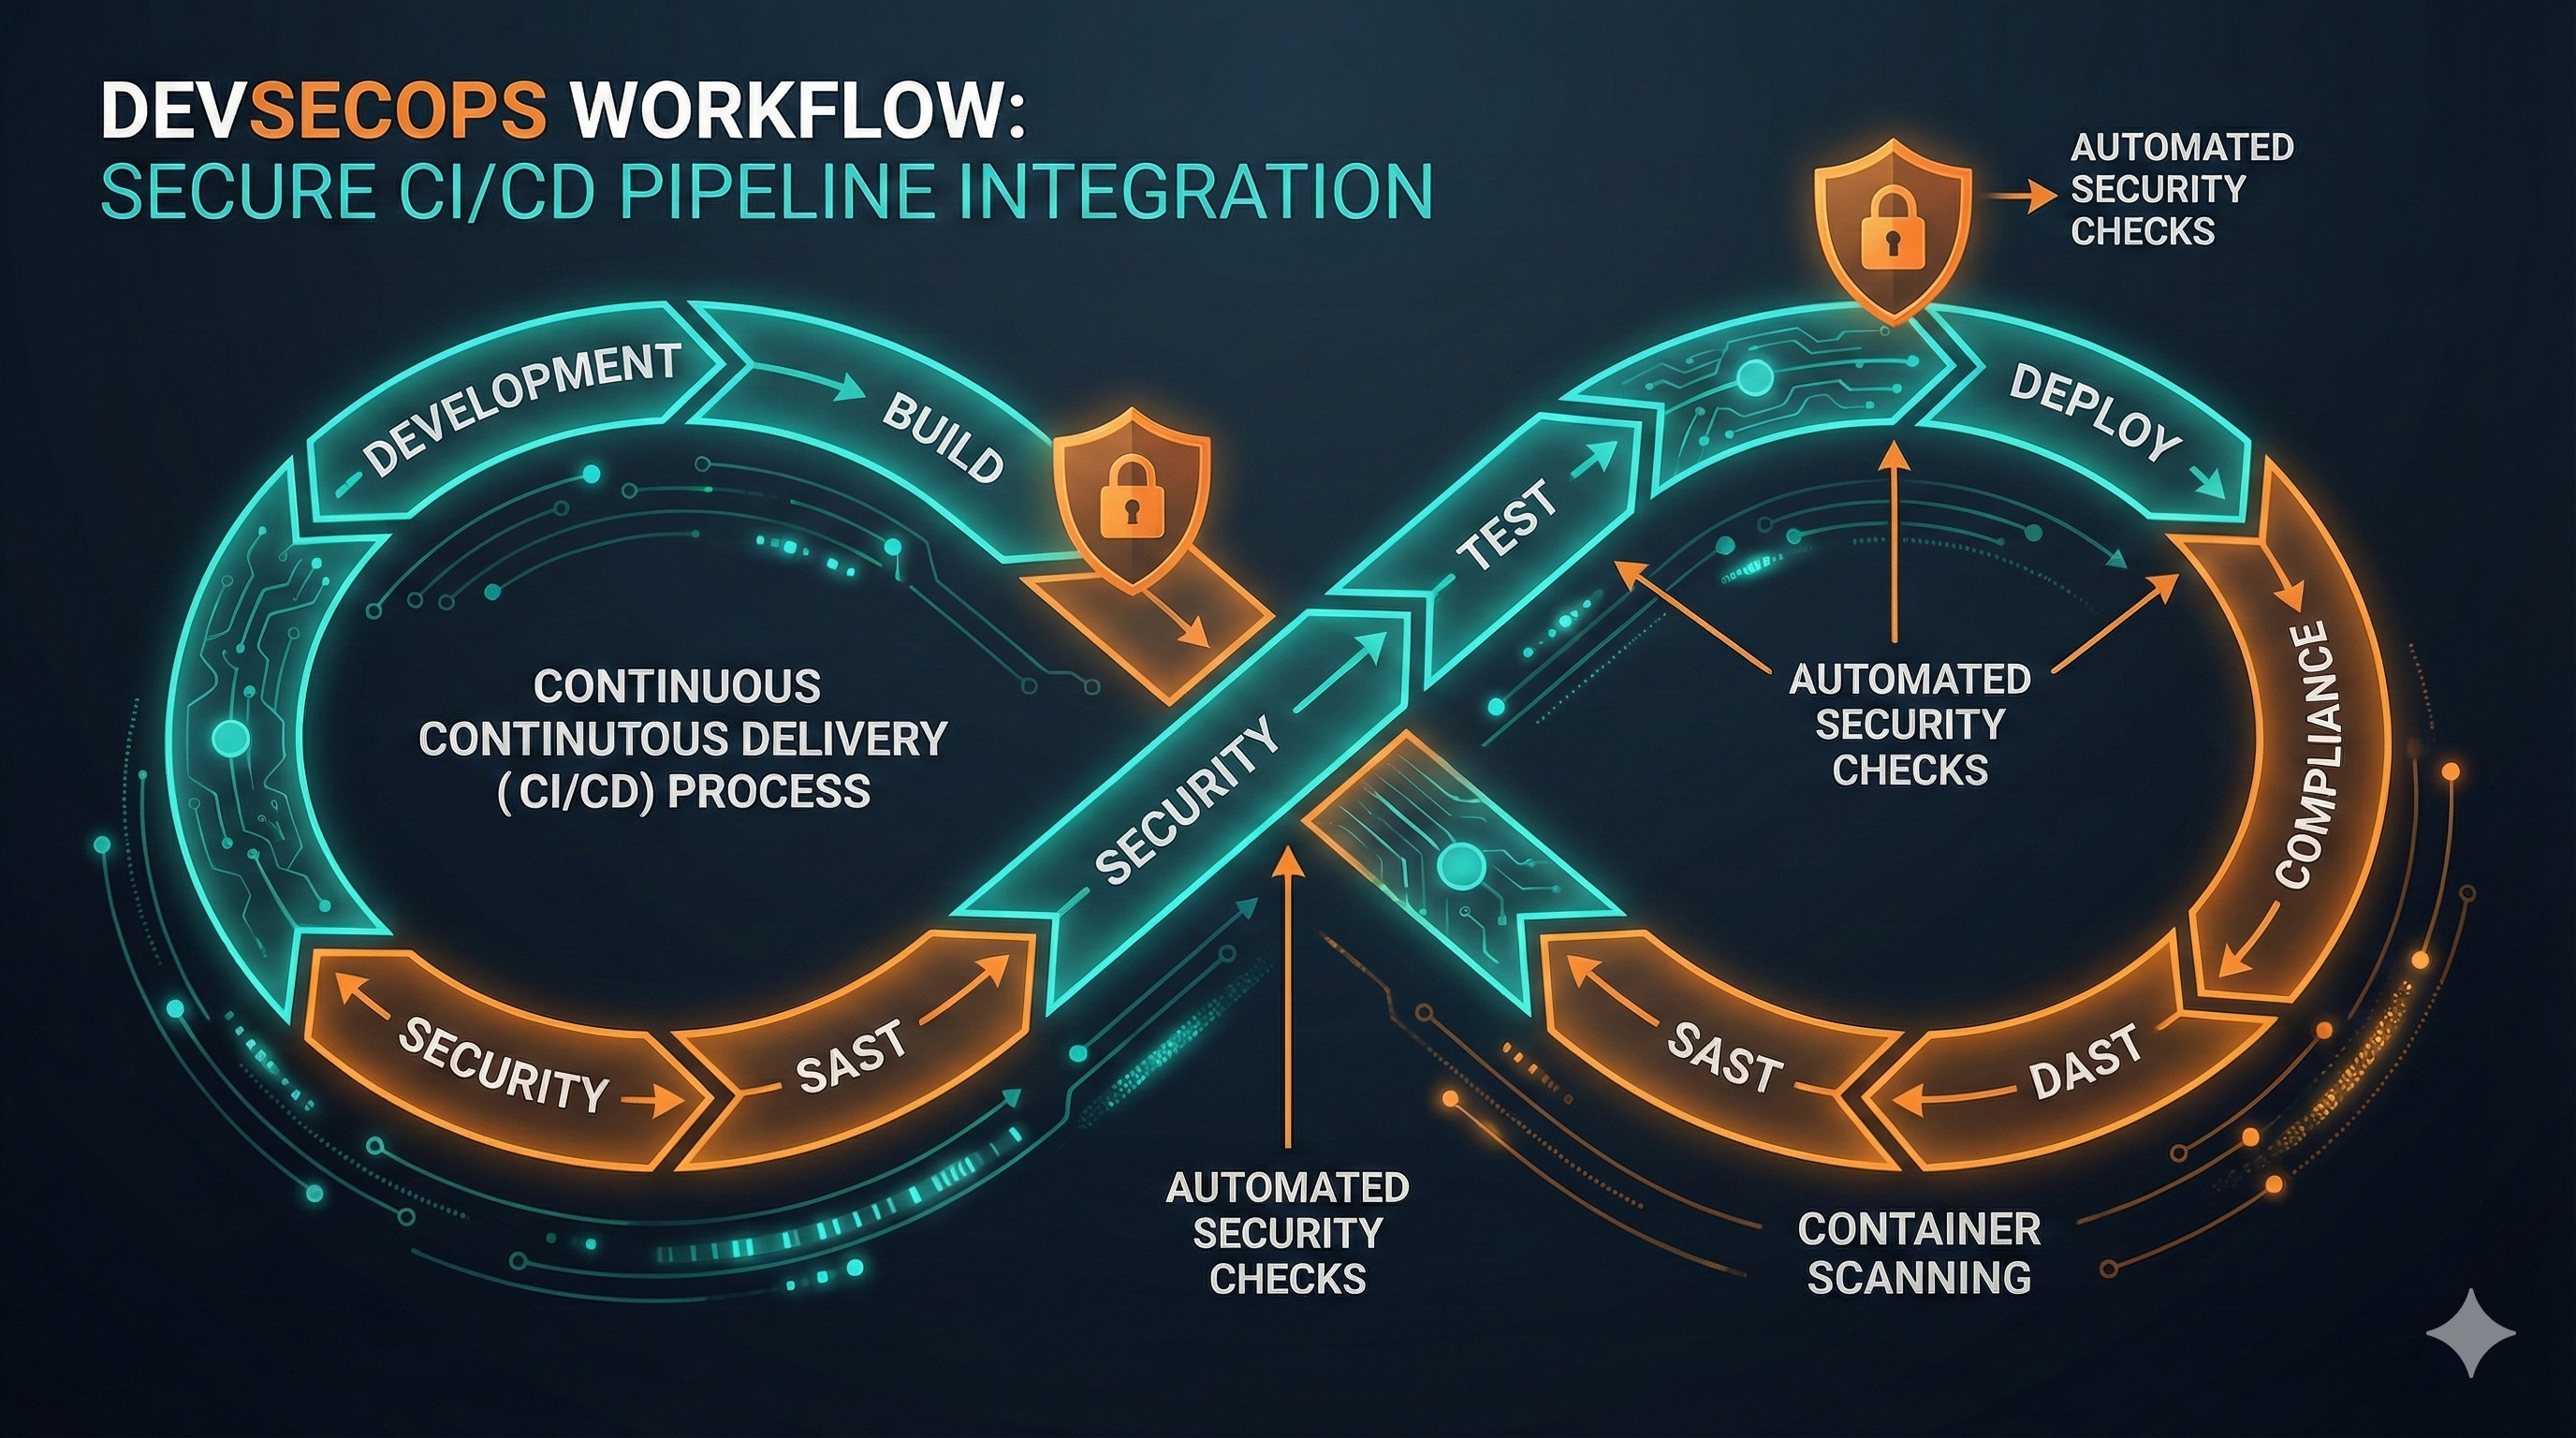
Auditors increasingly accept continuous, automated evidence: screenshots of CI checks, exports of access reviews, configuration scans. Wire your compliance tooling into the systems that already hold the truth, such as your identity provider, cloud accounts, and ticketing system. Manual evidence collection is where deadlines slip.
Compliance Is Not Security
A passing audit proves you met a baseline on a given day. Regulators know this, and so do attackers. Treat the framework as a floor: layer threat modeling, penetration testing, and monitoring on top so the controls that satisfy auditors also stop real attacks. In our experience the organizations that fail least are those that let security engineering drive compliance, not the other way around.
Make Ownership Explicit
Every control needs a named owner, a review cadence, and a documented exception path. When ownership is vague, controls decay silently between audits, and that decay is exactly what assessors find.
Conclusion
Compliance done well is a byproduct of good security engineering. If a framework deadline is approaching or your control library has drifted, talk to our team about building a program that survives audits year after year.